

New York Life Insurance Company
Jobs
Corporate Vice President - Cyber Security Incident Response Team Lead
New York Life Insurance Company
Corporate Vice President - Cyber Security Incident Response Team Lead
Be an Early Applicant
Leads the enterprise cybersecurity incident response function as senior incident commander and people leader. Directs containment, eradication, recovery, investigations, evidence handling, regulatory notifications, executive communications, crisis coordination, and post-incident improvement. Establishes incident response governance, playbooks, metrics, readiness objectives, and audit processes while coordinating security, technology, legal, compliance, business, vendors, and executive stakeholders. Builds and manages a multidisciplinary response team and maintains continuous coverage for high-impact incidents.
Location Designation: Hybrid - 3 days per week
Technology, Data, AI and Ventures:
Within the Tech, Data, AI, Ventures (TDAV) organization, our work is guided by a shared vision: deploying the power of technology, data, AI and ventures to accelerate sustainable competitive advantage for New York Life's businesses. We build solutions that power how we serve policy owners, agents, advisors and employees while delivering measurable business outcomes.
Across technology, data, AI, cyber, product, digital experience, architecture and infrastructure, TDAV combines the scale and investment of an industry leader, access to leading-edge technologies and the opportunity to help shape how a world-class financial services company competes in the AI era - all backed by the stability and purpose of a mutual company built to last.
Corporate Vice President, Cyber Security Incident Response Team Lead
Job Title: Corporate Vice President, Cyber Security Incident Management (CSIR) Lead
Level: MG3
Function: Cybersecurity
Location Designation: Onsite - 3 Days
Role Overview
The Cyber Incident Response (IR) Lead reports directly to the Chief Information Security Officer within the Cybersecurity organization and is accountable for New York Life's enterprise cyber incident response capability. The role establishes unified ownership from cyber incident activation through containment, eradication, secure recovery, and post-incident improvement, integrating specialized technical response with business, executive, legal, regulatory, and external coordination.
This position is both the senior incident commander and the people leader for the IR function. The IR Lead directs response the enterprise response to cybersecurity incidents of all severities, makes or drives time-critical response decisions, and ensures clear accountability across technical responders and business coordinators. The role is accountable for regulatory notification readiness, executive incident reporting, and coordination with legal, privacy, compliance, fraud, human resources, corporate communications, and business unit leadership
The individual will lead through ambiguity and operational pressure, exercising authority and composure during active incidents while maintaining the documentation discipline, evidentiary rigor, regulatory readiness, and stakeholder trust required in a regulated financial services environment.
What You'll Do
Enterprise Incident Command & Leadership
• Act as the enterprise Incident Commander for cybersecurity incidents, with end-to-end accountability from activation through recovery.
• Own incident declaration, severity classification, escalation, command structure, decision logging, executive checkpoints, and transition to post-incident activity.
• Direct cross-functional response across Security Operations, Threat Intelligence, digital forensics, identity, cloud, network, endpoint, infrastructure, applications, business teams, and external specialists.
• Lead containment, eradication, and secure recovery strategy in partnership with technology owners, balancing business impact, operational risk, evidence preservation, and adversary presence.
• Oversee evidence handling, chain of custody, and investigative documentation to a standard that supports legal, regulatory, and law enforcement requirements.
• Serve as the senior escalation point for cyber incident response with clear decision rights between SOC and IR as events move from alert investigation to confirmed incident response.
Team Leadership & People Management
• Build, develop, and lead a dedicated Cyber Incident Response function accountable to the CISO, combining specialized technical response capabilities with business and operational coordination and establishing clear end-to-end ownership from incident activation through secure recovery.
• Establish the IR capability roadmap, operating priorities, talent strategy, readiness objectives, and measurable outcomes; provide the CISO with a clear view of response readiness, material gaps, investment needs, and improvement priorities.
• Lead a multidisciplinary team expected to include technical responders focused on detection and containment, systems recovery and IR readiness, specialist response across cloud/identity/network, and business coordinators focused on stakeholder communications and operational continuity.
• Set and enforce clear expectations for response quality, documentation standards, communication cadence, and stakeholder handling.
• Balance team capacity across active incidents, investigations, program work, audit support, and regulatory deliverables.
• Serve as the senior escalation point and incident commander for the most complex, sensitive, or high-impact events.
• Maintain on-call rotations, escalation trees, and coverage models that provide continuous incident response availability across business and after hours.
Incident Management Program & Governance
• Own the cybersecurity incident management standard, response plan, playbooks, runbooks, and supporting procedures, including annual review, revision, and approval.
• Maintain alignment between the incident response program and NIST SP 800-61, the NIST Cybersecurity Framework, and applicable regulatory requirements.
• Enhance and maintain the severity taxonomy, incident categorization model, service level expectations, and quality standards for incident records.
• Ensure incident tickets, timelines, and case files are complete, accurate, defensible, and audit-ready.
• Support internal audit, external audit, regulatory examination, and third-party assessment activities related to incident response.
Regulatory, Legal & Notification Readiness
• Partner with the Office of the General Counsel, privacy, and compliance functions to assess notification obligations and support timely, accurate regulatory filings.
• Maintain working knowledge of financial services and insurance cybersecurity regulations, including state cybersecurity regulations with defined notification windows, state breach notification statutes, and applicable federal requirements.
• Track notification triggers, deadlines, and evidentiary requirements throughout the incident lifecycle, and escalate where determinations are time-critical.
• Coordinate third-party and vendor incident response, including service provider notification obligations, contractual security requirements, and supply chain events.
• Support legal hold, electronic discovery, and litigation readiness activities arising from cyber incidents.
Stakeholder Coordination & Crisis Communications
• Serve as the primary point of coordination between security operations, threat intelligence, technology owners, business stakeholders, control functions, and executive audiences during incidents.
• Prepare and deliver incident briefings to cybersecurity leadership, technology leadership, risk partners, and senior executives.
• Partner with corporate communications on internal and external messaging for incidents carrying reputational, customer, or media exposure.
• Coordinate with business continuity, disaster recovery, and crisis management functions when incidents require enterprise-level activation.
• Exercise extreme discretion and sound judgment when handling confidential investigations, sensitive findings, and need-to-know communications.
Reporting, Metrics & Executive Communications
• Develop and maintain incident reporting, dashboards, and executive-level materials summarizing incident volume, severity, themes, response performance, and remediation status.
• Define and track program metrics, including time to detect, time to contain, time to close, escalation accuracy, and recurrence rates.
• Translate complex technical incident detail into clear, practical, audience-appropriate communications.
• Identify recurring control gaps and organizational themes surfaced through incidents, and route them into remediation, issue management, and control improvement channels.
• Support recurring reporting to cybersecurity leadership, risk committees, senior management, and, as required, board-level audiences.
• Ensure reporting is accurate, balanced, actionable, and appropriately sensitive to audience and confidentiality considerations.
What You'll Bring
• Proven leadership of a cybersecurity incident response, digital forensics, security operations, or incident management capability, including direct people leadership.
• Demonstrated experience serving as Incident Commander or senior response lead for high-severity, cross-functional cybersecurity incidents in a large enterprise.
• Demonstrated technical depth in cybersecurity incident response sufficient to direct and challenge complex investigations, evaluate attacker activity and scope, assess containment and eradication options, and guide responders across endpoint, identity, cloud, network, applications, and enterprise technology environments.
• Working command of NIST SP 800-61 and the NIST Cybersecurity Framework, with experience operationalizing incident response standards, playbooks, severity models, exercises, and post-incident improvement.
• Experience coordinating across Security Operations, Threat Intelligence, digital forensics, identity and access management, cloud, network, endpoint, infrastructure, applications, business teams, vendors, legal, risk, privacy, compliance, and executive stakeholders.
• Experience with regulatory and breach-notification requirements applicable to financial services, insurance, or another highly regulated environment.
• Experience preparing executive-facing incident communications, metrics, dashboards, decision materials, and management reporting.
• Experience managing external IR/forensics retainers, vendors, statements of work, deliverables, and surge support.
• Experience managing cross-functional initiatives involving technology, cybersecurity, risk, legal, business, vendor, and executive stakeholders.
• Prior experience in a regulated financial services, insurance, or similarly complex enterprise environment preferred.
• Experience with incident management platforms, case management tooling, and security orchestration and automation preferred.
Knowledge and Education
• Bachelor's degree required or equivalent work experience.
• Eight or more years of cyber security or technology experience, including four or more years in incident response or incident management, and prior team leadership experience.
• Cyber security certification preferred, such as GCIH, GCFA, GCFE, CISSP, CISM, CRISC, or similar designation.
• Working knowledge of the NIST incident response lifecycle, the NIST Cybersecurity Framework, and common adversary frameworks such as MITRE ATT&CK.
• High-level understanding of cyber defense organizations, including security operations, incident response, threat intelligence, vulnerability management, identity, infrastructure, and application security functions.
• High-level understanding of enterprise technology functions, including application ownership, infrastructure, cloud, networking, end-user technology, and technology operations.
• Working knowledge of risk management, issue management, control remediation, and executive reporting practices.
Leadership, Communications and Collaboration
• Ability to communicate clearly and professionally with technical teams, business partners, risk stakeholders, vendors, and executive audiences.
• Demonstrated ability to assert authority, make decisions with incomplete information, maintain composure, and control the message during active incidents.
• Demonstrated ability to build trust and maintain positive working relationships, including in situations involving challenging findings, sensitive topics, or competing priorities.
• Strong organizational, analytical, written communication, and presentation skills.
• Ability to translate technical or complex cybersecurity concepts into practical business language.
• Proven ability to drive accountability and outcomes across teams without direct authority.
• Sound judgment, discretion, and professionalism when handling confidential or sensitive information.
• Self-motivated and detail-oriented, with the ability to manage shifting priorities in a dynamic execution environment.
• Ability to prioritize and deprioritize work based on risk, urgency, stakeholder impact, and
Job Level: LEVELMG3
Pay Transparency
Salary Range: $185,000-$264,500
Overtime eligible: Exempt
Discretionary bonus eligible: Yes
Sales bonus eligible: No
Actual base salary will be determined based on several factors but not limited to individual's experience, skills, qualifications, and job location. Additionally, employees are eligible for an annual discretionary bonus. In addition to base salary, employees may also be eligible to participate in an incentive program.
Company Overview
At New York Life, our 180-year legacy of purpose and integrity fuels our future. As we evolve into a more technology-, data-, and AI-enabled organization, we remain grounded in the values that drive lasting impact.
Our diverse business portfolio creates opportunities to make a difference across industries and communities-inviting bold thinking, collaborative problem-solving, and purpose-driven innovation. Here, you'll find the rare balance of long-standing stability and forward momentum, supported by an inclusive team that honors tradition while embracing progress.
As a Fortune 100 mutual company, we offer a place to grow your skills, contribute to meaningful work, and deliver solutions that matter. Your ideas drive what's next, and your growth powers it.
Our Benefits
We provide a full package of benefits for employees - and have unique offerings for a modern workforce, including leave programs, adoption assistance, and student loan repayment programs. Based on feedback from our employees, we continue to refine and add benefits to our offering, so that you can flourish both inside and outside of work.Click hereto discover more about our comprehensive benefit options or visit our NYL Benefits Site.
Our Commitment to Inclusion
At New York Life, fostering an inclusive workplace is fundamental to who we are and how we serve our communities. We have a longstanding commitment to creating an environment where individuals can contribute their best and succeed together. This foundation is rooted in our core values of humanity and integrity, ensuring that every employee feels valued and supported. By embracing a broad range of perspectives and experiences, we achieve greater success and fulfill our promise of providing financial security and peace of mind to families across all communities. Click here to learn more about New York Life's leadership in this space.
Recognized as one of Fortune's World's Most Admired Companies, New York Life is committed to improving local communities through a culture of employee giving and volunteerism, supported by the Foundation. We're proud that due to our mutuality, we operate in the best interests of our policy owners. To learn more about career opportunities at New York Life, please visit the Careers page of www.NewYorkLife.com.
Job Requisition ID: 94888
#BI-Hybrid
Technology, Data, AI and Ventures:
Within the Tech, Data, AI, Ventures (TDAV) organization, our work is guided by a shared vision: deploying the power of technology, data, AI and ventures to accelerate sustainable competitive advantage for New York Life's businesses. We build solutions that power how we serve policy owners, agents, advisors and employees while delivering measurable business outcomes.
Across technology, data, AI, cyber, product, digital experience, architecture and infrastructure, TDAV combines the scale and investment of an industry leader, access to leading-edge technologies and the opportunity to help shape how a world-class financial services company competes in the AI era - all backed by the stability and purpose of a mutual company built to last.
Corporate Vice President, Cyber Security Incident Response Team Lead
Job Title: Corporate Vice President, Cyber Security Incident Management (CSIR) Lead
Level: MG3
Function: Cybersecurity
Location Designation: Onsite - 3 Days
Role Overview
The Cyber Incident Response (IR) Lead reports directly to the Chief Information Security Officer within the Cybersecurity organization and is accountable for New York Life's enterprise cyber incident response capability. The role establishes unified ownership from cyber incident activation through containment, eradication, secure recovery, and post-incident improvement, integrating specialized technical response with business, executive, legal, regulatory, and external coordination.
This position is both the senior incident commander and the people leader for the IR function. The IR Lead directs response the enterprise response to cybersecurity incidents of all severities, makes or drives time-critical response decisions, and ensures clear accountability across technical responders and business coordinators. The role is accountable for regulatory notification readiness, executive incident reporting, and coordination with legal, privacy, compliance, fraud, human resources, corporate communications, and business unit leadership
The individual will lead through ambiguity and operational pressure, exercising authority and composure during active incidents while maintaining the documentation discipline, evidentiary rigor, regulatory readiness, and stakeholder trust required in a regulated financial services environment.
What You'll Do
Enterprise Incident Command & Leadership
• Act as the enterprise Incident Commander for cybersecurity incidents, with end-to-end accountability from activation through recovery.
• Own incident declaration, severity classification, escalation, command structure, decision logging, executive checkpoints, and transition to post-incident activity.
• Direct cross-functional response across Security Operations, Threat Intelligence, digital forensics, identity, cloud, network, endpoint, infrastructure, applications, business teams, and external specialists.
• Lead containment, eradication, and secure recovery strategy in partnership with technology owners, balancing business impact, operational risk, evidence preservation, and adversary presence.
• Oversee evidence handling, chain of custody, and investigative documentation to a standard that supports legal, regulatory, and law enforcement requirements.
• Serve as the senior escalation point for cyber incident response with clear decision rights between SOC and IR as events move from alert investigation to confirmed incident response.
Team Leadership & People Management
• Build, develop, and lead a dedicated Cyber Incident Response function accountable to the CISO, combining specialized technical response capabilities with business and operational coordination and establishing clear end-to-end ownership from incident activation through secure recovery.
• Establish the IR capability roadmap, operating priorities, talent strategy, readiness objectives, and measurable outcomes; provide the CISO with a clear view of response readiness, material gaps, investment needs, and improvement priorities.
• Lead a multidisciplinary team expected to include technical responders focused on detection and containment, systems recovery and IR readiness, specialist response across cloud/identity/network, and business coordinators focused on stakeholder communications and operational continuity.
• Set and enforce clear expectations for response quality, documentation standards, communication cadence, and stakeholder handling.
• Balance team capacity across active incidents, investigations, program work, audit support, and regulatory deliverables.
• Serve as the senior escalation point and incident commander for the most complex, sensitive, or high-impact events.
• Maintain on-call rotations, escalation trees, and coverage models that provide continuous incident response availability across business and after hours.
Incident Management Program & Governance
• Own the cybersecurity incident management standard, response plan, playbooks, runbooks, and supporting procedures, including annual review, revision, and approval.
• Maintain alignment between the incident response program and NIST SP 800-61, the NIST Cybersecurity Framework, and applicable regulatory requirements.
• Enhance and maintain the severity taxonomy, incident categorization model, service level expectations, and quality standards for incident records.
• Ensure incident tickets, timelines, and case files are complete, accurate, defensible, and audit-ready.
• Support internal audit, external audit, regulatory examination, and third-party assessment activities related to incident response.
Regulatory, Legal & Notification Readiness
• Partner with the Office of the General Counsel, privacy, and compliance functions to assess notification obligations and support timely, accurate regulatory filings.
• Maintain working knowledge of financial services and insurance cybersecurity regulations, including state cybersecurity regulations with defined notification windows, state breach notification statutes, and applicable federal requirements.
• Track notification triggers, deadlines, and evidentiary requirements throughout the incident lifecycle, and escalate where determinations are time-critical.
• Coordinate third-party and vendor incident response, including service provider notification obligations, contractual security requirements, and supply chain events.
• Support legal hold, electronic discovery, and litigation readiness activities arising from cyber incidents.
Stakeholder Coordination & Crisis Communications
• Serve as the primary point of coordination between security operations, threat intelligence, technology owners, business stakeholders, control functions, and executive audiences during incidents.
• Prepare and deliver incident briefings to cybersecurity leadership, technology leadership, risk partners, and senior executives.
• Partner with corporate communications on internal and external messaging for incidents carrying reputational, customer, or media exposure.
• Coordinate with business continuity, disaster recovery, and crisis management functions when incidents require enterprise-level activation.
• Exercise extreme discretion and sound judgment when handling confidential investigations, sensitive findings, and need-to-know communications.
Reporting, Metrics & Executive Communications
• Develop and maintain incident reporting, dashboards, and executive-level materials summarizing incident volume, severity, themes, response performance, and remediation status.
• Define and track program metrics, including time to detect, time to contain, time to close, escalation accuracy, and recurrence rates.
• Translate complex technical incident detail into clear, practical, audience-appropriate communications.
• Identify recurring control gaps and organizational themes surfaced through incidents, and route them into remediation, issue management, and control improvement channels.
• Support recurring reporting to cybersecurity leadership, risk committees, senior management, and, as required, board-level audiences.
• Ensure reporting is accurate, balanced, actionable, and appropriately sensitive to audience and confidentiality considerations.
What You'll Bring
• Proven leadership of a cybersecurity incident response, digital forensics, security operations, or incident management capability, including direct people leadership.
• Demonstrated experience serving as Incident Commander or senior response lead for high-severity, cross-functional cybersecurity incidents in a large enterprise.
• Demonstrated technical depth in cybersecurity incident response sufficient to direct and challenge complex investigations, evaluate attacker activity and scope, assess containment and eradication options, and guide responders across endpoint, identity, cloud, network, applications, and enterprise technology environments.
• Working command of NIST SP 800-61 and the NIST Cybersecurity Framework, with experience operationalizing incident response standards, playbooks, severity models, exercises, and post-incident improvement.
• Experience coordinating across Security Operations, Threat Intelligence, digital forensics, identity and access management, cloud, network, endpoint, infrastructure, applications, business teams, vendors, legal, risk, privacy, compliance, and executive stakeholders.
• Experience with regulatory and breach-notification requirements applicable to financial services, insurance, or another highly regulated environment.
• Experience preparing executive-facing incident communications, metrics, dashboards, decision materials, and management reporting.
• Experience managing external IR/forensics retainers, vendors, statements of work, deliverables, and surge support.
• Experience managing cross-functional initiatives involving technology, cybersecurity, risk, legal, business, vendor, and executive stakeholders.
• Prior experience in a regulated financial services, insurance, or similarly complex enterprise environment preferred.
• Experience with incident management platforms, case management tooling, and security orchestration and automation preferred.
Knowledge and Education
• Bachelor's degree required or equivalent work experience.
• Eight or more years of cyber security or technology experience, including four or more years in incident response or incident management, and prior team leadership experience.
• Cyber security certification preferred, such as GCIH, GCFA, GCFE, CISSP, CISM, CRISC, or similar designation.
• Working knowledge of the NIST incident response lifecycle, the NIST Cybersecurity Framework, and common adversary frameworks such as MITRE ATT&CK.
• High-level understanding of cyber defense organizations, including security operations, incident response, threat intelligence, vulnerability management, identity, infrastructure, and application security functions.
• High-level understanding of enterprise technology functions, including application ownership, infrastructure, cloud, networking, end-user technology, and technology operations.
• Working knowledge of risk management, issue management, control remediation, and executive reporting practices.
Leadership, Communications and Collaboration
• Ability to communicate clearly and professionally with technical teams, business partners, risk stakeholders, vendors, and executive audiences.
• Demonstrated ability to assert authority, make decisions with incomplete information, maintain composure, and control the message during active incidents.
• Demonstrated ability to build trust and maintain positive working relationships, including in situations involving challenging findings, sensitive topics, or competing priorities.
• Strong organizational, analytical, written communication, and presentation skills.
• Ability to translate technical or complex cybersecurity concepts into practical business language.
• Proven ability to drive accountability and outcomes across teams without direct authority.
• Sound judgment, discretion, and professionalism when handling confidential or sensitive information.
• Self-motivated and detail-oriented, with the ability to manage shifting priorities in a dynamic execution environment.
• Ability to prioritize and deprioritize work based on risk, urgency, stakeholder impact, and
Job Level: LEVELMG3
Pay Transparency
Salary Range: $185,000-$264,500
Overtime eligible: Exempt
Discretionary bonus eligible: Yes
Sales bonus eligible: No
Actual base salary will be determined based on several factors but not limited to individual's experience, skills, qualifications, and job location. Additionally, employees are eligible for an annual discretionary bonus. In addition to base salary, employees may also be eligible to participate in an incentive program.
Company Overview
At New York Life, our 180-year legacy of purpose and integrity fuels our future. As we evolve into a more technology-, data-, and AI-enabled organization, we remain grounded in the values that drive lasting impact.
Our diverse business portfolio creates opportunities to make a difference across industries and communities-inviting bold thinking, collaborative problem-solving, and purpose-driven innovation. Here, you'll find the rare balance of long-standing stability and forward momentum, supported by an inclusive team that honors tradition while embracing progress.
As a Fortune 100 mutual company, we offer a place to grow your skills, contribute to meaningful work, and deliver solutions that matter. Your ideas drive what's next, and your growth powers it.
Our Benefits
We provide a full package of benefits for employees - and have unique offerings for a modern workforce, including leave programs, adoption assistance, and student loan repayment programs. Based on feedback from our employees, we continue to refine and add benefits to our offering, so that you can flourish both inside and outside of work.Click hereto discover more about our comprehensive benefit options or visit our NYL Benefits Site.
Our Commitment to Inclusion
At New York Life, fostering an inclusive workplace is fundamental to who we are and how we serve our communities. We have a longstanding commitment to creating an environment where individuals can contribute their best and succeed together. This foundation is rooted in our core values of humanity and integrity, ensuring that every employee feels valued and supported. By embracing a broad range of perspectives and experiences, we achieve greater success and fulfill our promise of providing financial security and peace of mind to families across all communities. Click here to learn more about New York Life's leadership in this space.
Recognized as one of Fortune's World's Most Admired Companies, New York Life is committed to improving local communities through a culture of employee giving and volunteerism, supported by the Foundation. We're proud that due to our mutuality, we operate in the best interests of our policy owners. To learn more about career opportunities at New York Life, please visit the Careers page of www.NewYorkLife.com.
Job Requisition ID: 94888
#BI-Hybrid
New York Life Insurance Company New York, New York, USA Office

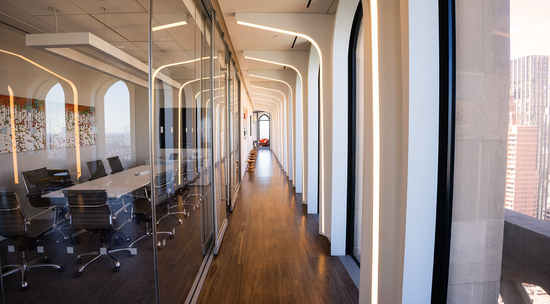
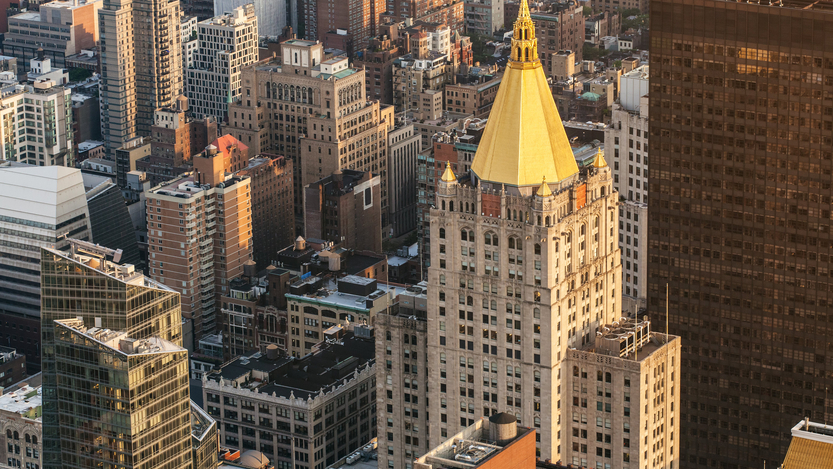

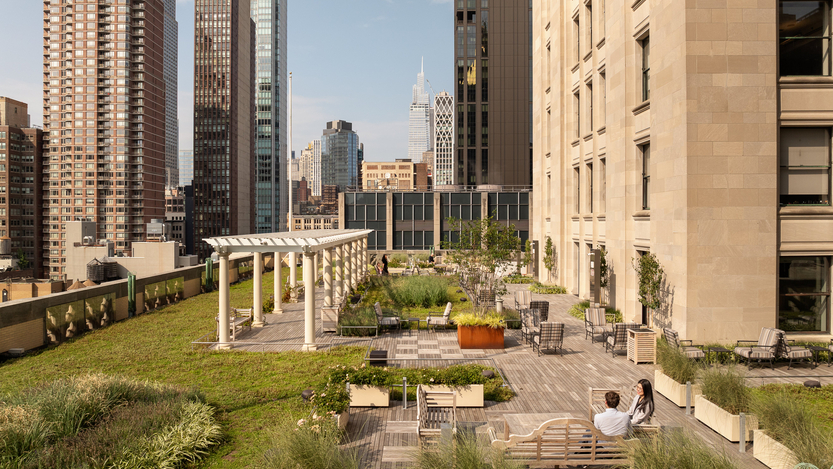

51 Madison Avenue, New York, NY, United States, 10010
New York Life Insurance Company Jersey City, New Jersey, USA Office
New York Life Insurance Company Jersey City, NJ Office
30 Hudson Street , Jersey City, New Jersey, United States, 07302
Similar Jobs at New York Life Insurance Company
Artificial Intelligence • Cloud • Fintech • Information Technology • Insurance • Financial Services • Big Data Analytics
Manages an assigned long-term disability claims caseload by evaluating eligibility, reviewing medical and contractual information, calculating benefits, and making timely claim decisions. Develops strategic case plans, communicates with customers, employers, physicians, attorneys, and vocational counselors, and facilitates return-to-work opportunities. Maintains claim documentation, meets service and performance standards, follows compliance procedures, and handles complex customer interactions while coordinating with internal clinical and business partners.
Top Skills:
ExcelMS OfficeMicrosoft OutlookMicrosoft Word
Artificial Intelligence • Cloud • Fintech • Information Technology • Insurance • Financial Services • Big Data Analytics
Manage investment strategy and asset allocation for insurance product portfolios within New York Life’s General Account. Partner with insurance businesses, finance leaders, and investment teams on asset-liability management, pricing, capital management, reinsurance, liquidity, portfolio construction, and risk resiliency. Lead asset-liability committee meetings, develop investment assumptions and reinvestment strategies, ensure regulatory and policy alignment, and present recommendations to executives.
Artificial Intelligence • Cloud • Fintech • Information Technology • Insurance • Financial Services • Big Data Analytics
Provides high-level administrative support to multiple executive officers and their teams. Responsibilities include calendar management, meeting and event coordination, materials preparation, expense reconciliation, onboarding assistance, organizational chart maintenance, special projects, sensitive information handling, and meeting follow-up. The role also coordinates stakeholders, rooms, presentations, A/V needs, and technology support while serving as backup for other administrative assistants.
Top Skills:
Ai ToolsExcelMicrosoft Office SuiteMicrosoft OutlookMicrosoft PowerpointMicrosoft Word
What you need to know about the NYC Tech Scene
As the undisputed financial capital of the world, New York City is an epicenter of startup funding activity. The city has a thriving fintech scene and is a major player in verticals ranging from AI to biotech, cybersecurity and digital media. It also has universities like NYU, Columbia and Cornell Tech attracting students and researchers from across the globe, providing the ecosystem with a constant influx of world-class talent. And its East Coast location and three international airports make it a perfect spot for European companies establishing a foothold in the United States.
Key Facts About NYC Tech
- Number of Tech Workers: 549,200; 6% of overall workforce (2024 CompTIA survey)
- Major Tech Employers: Capgemini, Bloomberg, IBM, Spotify
- Key Industries: Artificial intelligence, Fintech
- Funding Landscape: $25.5 billion in venture capital funding in 2024 (Pitchbook)
- Notable Investors: Greycroft, Thrive Capital, Union Square Ventures, FirstMark Capital, Tiger Global Management, Tribeca Venture Partners, Insight Partners, Two Sigma Ventures
- Research Centers and Universities: Columbia University, New York University, Fordham University, CUNY, AI Now Institute, Flatiron Institute, C.N. Yang Institute for Theoretical Physics, NASA Space Radiation Laboratory
